IT infrastructure guide
Types of Network and How to Set Up a Small Business Network
In this guide
- Types of network explained
- Core components of an office network
- Office network design principles
- VLAN for small office networks
- IP addressing plan
- Internet, redundancy and branch links
- Wi-Fi design basics
- Security baseline
- Small business network setup: step by step
- Monitoring, documentation and growth
- Common mistakes
- FAQ
- Conclusion
Before you buy a single switch, it helps to understand the main types of network and which of them your office actually needs. This guide explains LAN, WAN, WLAN, SD-WAN and VPN in plain English, then walks through a practical small business network setup for a UAE office: firewall, switching, VLANs, Wi-Fi, backup internet, IP planning and documentation.
Key takeaways
- Most small offices need three network types working together: a wired LAN, a wireless LAN and a WAN connection to the internet and any branches.
- A router connects your network to other networks; a switch connects devices inside your network. A business firewall usually handles the routing role.
- Separate staff, guest, voice, CCTV and server traffic using VLANs, even in a 15-person office.
- Plan IP addressing, cabling and rack space for at least three years of growth, not just day one.
- A second internet line from a different provider is the cheapest insurance against a lost working day.
- Document everything: IP plan, VLAN list, passwords in a vault and a simple diagram.
Types of network explained
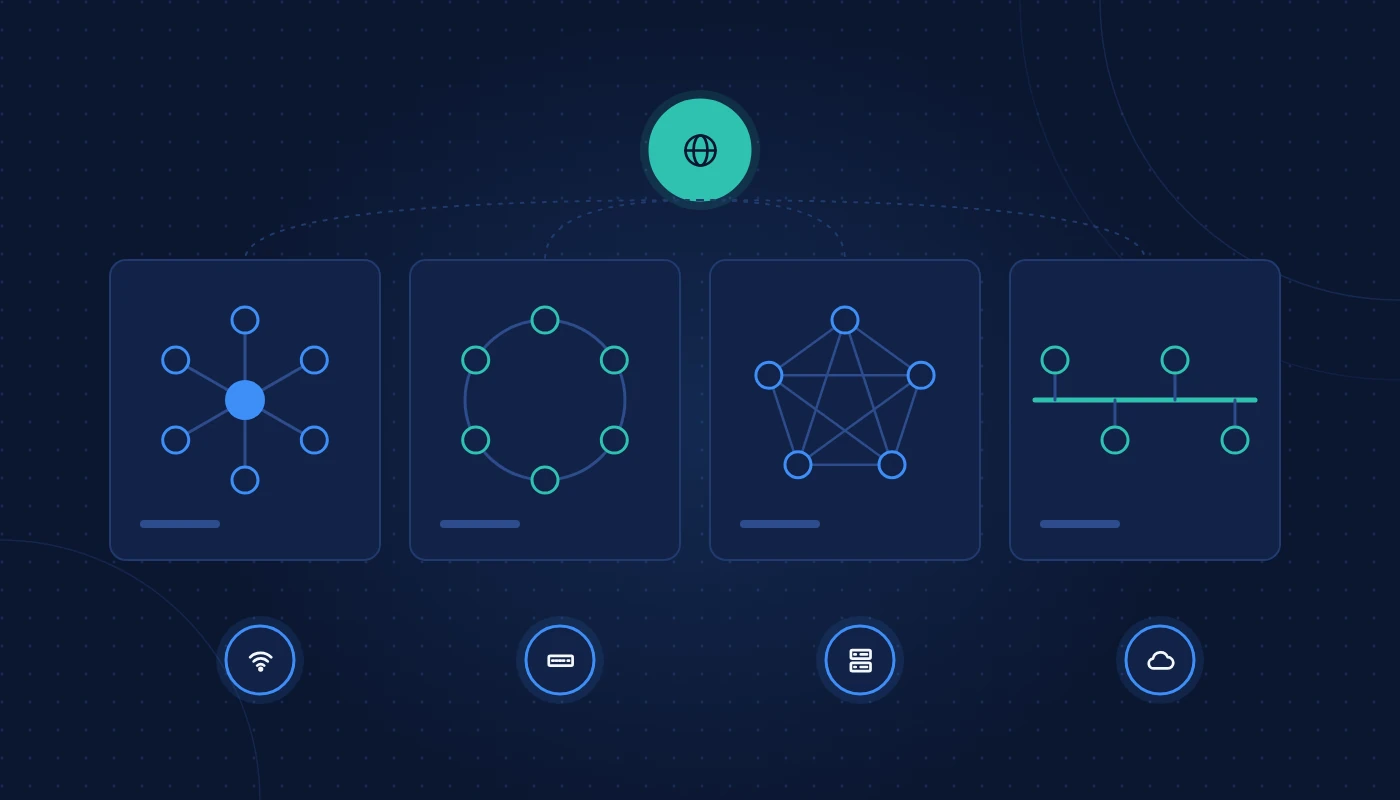
Networks are usually classified by the area they cover and the job they do. Here are the types of network a business owner is most likely to hear about.
| Network type | Full name | Coverage | Typical business use |
|---|---|---|---|
| PAN | Personal Area Network | A few metres | Bluetooth headsets, phone to laptop |
| LAN | Local Area Network | One office or floor | Desktops, printers, servers, phones |
| WLAN | Wireless LAN | One office or floor | Laptops, phones, tablets over Wi-Fi |
| CAN | Campus Area Network | Several buildings on one site | Schools, hospitals, industrial yards |
| MAN | Metropolitan Area Network | A city | Linking offices across Dubai or Abu Dhabi |
| WAN | Wide Area Network | Cities and countries | Connecting branches, the internet itself |
| SD-WAN | Software-Defined WAN | Multi-site | Smart routing over several internet links |
| VPN | Virtual Private Network | Overlay on the internet | Secure remote access and site-to-site links |
| SAN | Storage Area Network | Server room | Dedicated storage traffic for servers |
LAN vs WAN
The LAN vs WAN distinction is the one that matters most for small businesses. A LAN is the network inside your premises: the cables, switches and Wi-Fi that let your devices talk to each other and to local printers or servers. You own and control it.
A WAN connects locations together over distances you do not control. Your internet connection is a WAN link, and so is a link between your Dubai head office and a Sharjah warehouse. WAN links are usually provided by a telecom operator, which in the UAE means e& (formerly Etisalat) or du for most fixed connections.
In practice: the LAN is about speed and organisation inside the office; the WAN is about reliability, security and bandwidth between sites.
WLAN and why it is its own design problem
Wireless LAN is technically part of your LAN, but it has its own challenges: interference, coverage, roaming and security. In UAE offices with glass partitions, concrete cores and neighbouring tenants all broadcasting Wi-Fi, design matters more than the access point brand. Our office Wi-Fi design guide goes deeper on this.
SD-WAN and VPN
SD-WAN sits on top of multiple internet connections and steers traffic intelligently: video calls over the best-performing line, backups over the cheaper one, and automatic failover when a link drops. It is increasingly common for businesses with two or more branches.
A VPN creates an encrypted tunnel across the internet. Site-to-site VPNs link offices; remote-access VPNs (or newer zero trust alternatives) let staff connect securely from home. Note that the UAE regulates VPN use; businesses using VPNs for legitimate corporate access are generally fine, but check current TDRA guidance for your use case.
Core components of an office network
Every small business network setup is built from the same handful of parts.
Network switch vs router
The network switch vs router question confuses many people because consumer “routers” combine both.
- A switch connects devices within the same network. It forwards traffic between your PCs, printers, access points and servers using MAC addresses. Managed switches also handle VLANs, Power over Ethernet (PoE) and traffic priority.
- A router connects different networks together, such as your LAN and the internet, or one VLAN and another. It uses IP addresses to decide where traffic goes.
In a business, the routing role is normally performed by the firewall, which also inspects and filters traffic. The ISP router is often left in a simple “bridge” mode or used only as the handoff point. If you are choosing switches, our article on managed vs unmanaged switches explains why a managed switch is the right default for business.
Firewall
The firewall is the gatekeeper between your network and the internet, and between internal segments. A next-generation firewall adds application control, intrusion prevention, web filtering and VPN. For most small offices this is the most important single device on the network, which is why ongoing firewall management services are worth considering rather than “install and forget”.
Wireless access points
Business access points are ceiling-mounted, powered by PoE and centrally managed. They support multiple SSIDs mapped to VLANs, seamless roaming and proper guest isolation. Consumer mesh kits rarely do all of that well.
Cabling and rack
Copper cabling (Cat6 or Cat6a) runs from each desk and access point back to a patch panel in a rack. Good structured cabling is the foundation everything else relies on; poor cabling causes intermittent faults that are hard to diagnose later.
Supporting kit
- UPS to keep the firewall, switches and ISP equipment running through short outages
- Patch panels and cable management for tidy, labelled connections
- Cooling or ventilation for the comms cabinet, which matters in UAE summers
Office network design principles
Good office network design is less about buying premium gear and more about making a few structural decisions correctly at the start.
Design for segments, not a flat network
A “flat” network puts every device in one big group. It is simple, but a compromised laptop can then reach the accounting server, the CCTV recorder and the guest Wi-Fi users. Segmentation limits that blast radius.
Size for growth
Plan switch ports at roughly 20–30% above current need, and run spare cable drops to likely future desk positions. Re-cabling an occupied office in a Dubai tower usually means out-of-hours work and building management approvals.
Keep the core simple
For a single-site office under about 100 users, a firewall plus one or two stacked managed switches is usually enough. You do not need a separate core and distribution layer.
Plan for power and heat
Count PoE devices (access points, IP phones, cameras) and choose switches with enough PoE budget. Place the rack where it can be ventilated; a sealed cupboard next to a sunny window will cook equipment in July and August.
A typical small office layout
| Layer | Device | Role |
|---|---|---|
| Internet edge | ISP router/ONT (primary) + 4G/5G or second fibre (backup) | WAN connectivity |
| Security | Next-generation firewall | Routing, NAT, VPN, filtering, inter-VLAN rules |
| Switching | 1–2 managed PoE switches | Connect and power devices, carry VLANs |
| Wireless | 2–6 ceiling access points | Staff, guest and IoT SSIDs |
| Endpoints | PCs, laptops, printers, phones, cameras | Users and devices |
| Services | NAS or server, CCTV recorder | Local storage and recording |
VLAN for small office networks
A VLAN (Virtual LAN) splits one physical switch into several logical networks. Devices in different VLANs cannot talk to each other unless the firewall allows it. Using a VLAN for a small office is one of the cheapest security improvements you can make, because managed switches already support it.
A sample VLAN plan
| VLAN ID | Name | Who/what | Rules |
|---|---|---|---|
| 10 | Management | Switches, APs, firewall admin | Admin access only |
| 20 | Staff | Company laptops and desktops | Internet + servers + printers |
| 30 | Servers | NAS, file server, app server | Accessible from Staff on needed ports |
| 40 | Voice | IP phones | QoS priority, limited access |
| 50 | CCTV | Cameras and recorder | No internet, viewing from Staff only |
| 60 | Guest | Visitors’ devices | Internet only, client isolation |
| 70 | IoT | Smart TVs, displays, access control | Internet as needed, no access to Staff |
How VLANs work in practice
Each switch port is assigned to a VLAN (an “access port”) or carries several VLANs (a “trunk”, for example to an access point or another switch). The firewall has an interface or sub-interface in each VLAN and enforces rules between them.
On Wi-Fi, each SSID maps to a VLAN: “Company” to Staff, “Company-Guest” to Guest. That way a visitor in your meeting room never shares a network with your finance team.
IP addressing plan
An IP plan prevents conflicts and makes troubleshooting far easier. Use private address ranges and give each VLAN its own subnet that matches its VLAN ID, for example 10.10.20.0/24 for VLAN 20 and 10.10.30.0/24 for VLAN 30.
A few practical rules:
- Avoid 192.168.0.0/24 and 192.168.1.0/24. Home routers use them, which causes clashes when staff connect over VPN from home.
- Reserve a block in each subnet for static devices (printers, servers, switches) and leave the rest for DHCP.
- Keep DHCP leases sensible: shorter for guest networks, longer for staff.
- Record every static address in your documentation, not on a sticky note on the rack.
Internet, redundancy and branch links
Primary and backup internet
Most UAE offices take business fibre from e& or du, depending on which operator serves the building. Many towers and free zones are served by only one operator for fixed lines, so check before signing a lease for your specific building.
A backup line is essential. Options include a second fixed line (from the other operator, where available) or a business 4G/5G router. Connect both to the firewall and configure automatic failover so users barely notice an outage.
Static IP and inbound services
If you host anything that must be reachable from outside, such as a VPN, a remote desktop gateway or a CCTV viewer, request a static public IP from your ISP. Never expose remote desktop directly to the internet; put it behind a VPN or a zero trust gateway.
Connecting branches
For two or more sites, use site-to-site VPN over the internet, or SD-WAN when you have several sites and multiple links per site. A trading business with a Deira showroom, an Al Quoz warehouse and an Abu Dhabi branch, for example, can run one VPN mesh so all sites reach the central ERP server securely.
Wi-Fi design basics
Wireless design deserves its own survey, but a few rules apply everywhere:
- Plan by capacity, not just coverage. A boardroom with 20 laptops needs more access points than a corridor of the same size.
- Use 5 GHz and 6 GHz (Wi-Fi 6E/7) for staff; leave 2.4 GHz mainly for older or IoT devices.
- Mount access points on the ceiling, away from metal ducts and structural columns.
- Use WPA3 or WPA2-Enterprise for staff networks where possible, and a separate captive portal or simple password for guests.
If you would rather not design it yourself, our enterprise Wi-Fi solutions team can run a survey and heat-map before installation.
Security baseline
A small office network does not need to be complicated to be secure. Apply this baseline:
- Change every default password on firewalls, switches, access points and printers
- Keep firmware updated on a regular schedule
- Disable unused switch ports or put them in an isolated VLAN
- Turn on firewall features such as IPS and web filtering, and review logs
- Use multi-factor authentication for VPN and admin access
- Back up device configurations after every change
- Restrict management interfaces to the management VLAN
Some industries have additional obligations. Entities working with government or critical sectors may need to align with UAE Information Assurance standards, which affects segmentation and logging requirements.
Small business network setup: step by step
This is the sequence we follow for a typical 10–60 user office.
- Survey the space. Walk the floor plan, count desks, meeting rooms, printers, cameras and phones. Note where the comms room or cabinet will go and how it will be cooled.
- Confirm internet availability. Check which operator serves the building and order primary and backup connections early; lead times can be several weeks.
- Design the logical network. Write down VLANs, subnets, SSIDs and firewall rules before anything is installed.
- Install cabling. Run Cat6 or Cat6a to every desk, access point and camera location, terminate on patch panels and label both ends.
- Mount the rack and power. Install the rack, UPS, patch panels and cable management. Confirm dedicated power circuits.
- Configure the firewall. Set up WAN failover, VLAN interfaces, DHCP, DNS, VPN, security profiles and inter-VLAN rules.
- Configure switches. Assign VLANs to ports, set trunks, enable PoE where needed and apply security settings.
- Deploy Wi-Fi. Mount access points, map SSIDs to VLANs and tune channels and power.
- Connect endpoints. Join PCs, printers, phones and cameras, testing each VLAN for correct access.
- Test failover and security. Pull the primary internet cable, check failover, confirm guests cannot reach internal systems.
- Document and hand over. Produce the diagram, IP plan, VLAN table and credentials, stored securely.
For a new fit-out, this usually runs alongside the wider IT setup for a new office, including phones, printers and user onboarding.
Pre-go-live checklist
☐ Primary and backup internet installed and failover tested
☐ Firewall firmware updated and admin access restricted
☐ VLANs created and tested for correct isolation
☐ Guest Wi-Fi isolated from all internal networks
☐ All cable runs labelled and tested
☐ UPS connected and runtime checked
☐ Switch and firewall configurations backed up
☐ Default passwords changed on every device
☐ Network diagram and IP plan documented
☐ Monitoring and alerting switched on
Monitoring, documentation and growth
Monitor before users complain
A network that is not monitored is only “working” until someone notices it is not. Basic monitoring tracks internet link status, switch port errors, access point health and firewall resource usage, and alerts you before users raise tickets. You can run a tool yourself or use managed network services that watch it for you.
Documentation that actually helps
Keep a one-page network diagram, an IP and VLAN table, a list of ISP account numbers and support contacts, and device credentials in a password manager. When a new engineer or provider takes over, this saves hours.
Planning for growth
As you grow past one floor or one site, consider stackable switches, a controller or cloud-managed platform for Wi-Fi, and SD-WAN between branches. Many UAE businesses standardise on one vendor ecosystem to keep management simple. If you are evaluating Cisco, for example, our Cisco UAE page covers both cloud-managed Meraki and traditional Catalyst options.
When the network becomes business-critical across several sites, it is worth bringing in specialist network solutions support for design reviews rather than adding kit piece by piece.
Common mistakes
- Relying on the ISP router. It was not designed to be your security boundary or to manage VLANs.
- One flat network for everything. Guests, cameras and finance laptops should never share a segment.
- Buying unmanaged switches to save effort. They cannot do VLANs, monitoring or PoE management properly.
- Skipping the backup internet line. One fibre cut in a construction zone can stop the whole office.
- Using 192.168.1.x for the office. It clashes with home networks over VPN.
- Ignoring heat. Comms cabinets without ventilation fail early in UAE summers.
- No documentation. If only one person knows the passwords, you have a single point of failure.
- Placing Wi-Fi by guesswork. Coverage looks fine on day one and collapses when the office fills up.
Frequently asked questions
What are the main types of network for a business?
The main types are LAN (wired local network), WLAN (Wi-Fi), WAN (connections between sites and to the internet), VPN (secure tunnels over the internet) and SD-WAN (intelligent management of multiple WAN links). Larger organisations may also use MAN, CAN and SAN.
What is the difference between LAN vs WAN?
A LAN connects devices within one location and is owned by you. A WAN connects multiple locations over long distances, usually using links provided by a telecom operator, including your internet connection.
What is the difference between a network switch vs router?
A switch connects devices inside the same network; a router connects separate networks, such as your office and the internet. In business networks, a firewall typically performs the routing role.
Do I need a VLAN for a small office?
Yes, in most cases. Even a 10-person office benefits from separating staff, guest Wi-Fi and devices such as cameras. It improves security and performance, and managed switches support it already.
How long does a small business network setup take?
For a small single-site office with cabling already in place, configuration can take a few days. A new fit-out with cabling, internet orders and Wi-Fi surveys usually takes several weeks, largely driven by ISP lead times and building approvals.
Should I choose cloud-managed or traditional network equipment?
Cloud-managed platforms are easier for small teams and multi-site businesses because everything is visible from one dashboard. Traditional equipment offers more granular control and no ongoing cloud licence dependency. Both are valid; choose based on your team’s skills and growth plans.
What is the best office network design for 50 users?
A next-generation firewall with dual internet, one or two stacked managed PoE switches, four to eight ceiling access points depending on the floor plan, a segmented VLAN plan and a UPS-protected rack is a solid design for a 50-user office.
Conclusion
Understanding the types of network is the starting point; designing them to work together is what keeps an office productive. Start with a segmented LAN, a properly managed firewall, a second internet line and Wi-Fi designed for capacity, then document and monitor it so it stays reliable as you grow.
For more practical infrastructure advice, explore our IT infrastructure guides or ask us to review your current setup.
Ready to build a network that grows with your business?
More IT infrastructure guides
What Is IT Asset Management? Best Practices for Lifecycle, Register and Tools
What IT asset management is and how to do it well: asset register template, hardware inventory list, lifecycle stages, software licences, disposal and tools.
What Is Virtualization? Types, Hyper-V vs VMware and How to Plan
What virtualization is, the main types, its role in cloud computing, Hyper-V vs VMware compared, VMware alternatives and how to plan a project.
NAS vs SAN, RAID and Server Sizing: A Practical Guide for Business
Choose the right business server and storage: NAS vs SAN vs DAS, rack vs tower servers, RAID levels, sizing, backups and when to use the cloud.